AI INDUSTRY assessment
Security auditability of a publishing system: public interface boundaries, permissions, publication gates and evidence provenance.
Requirements and assessment plan →REFERENCES FOR AUDITABLE AI SYSTEMS
A shared foundation for people and agents who need to understand AI systems and independently assess the evidence behind them.
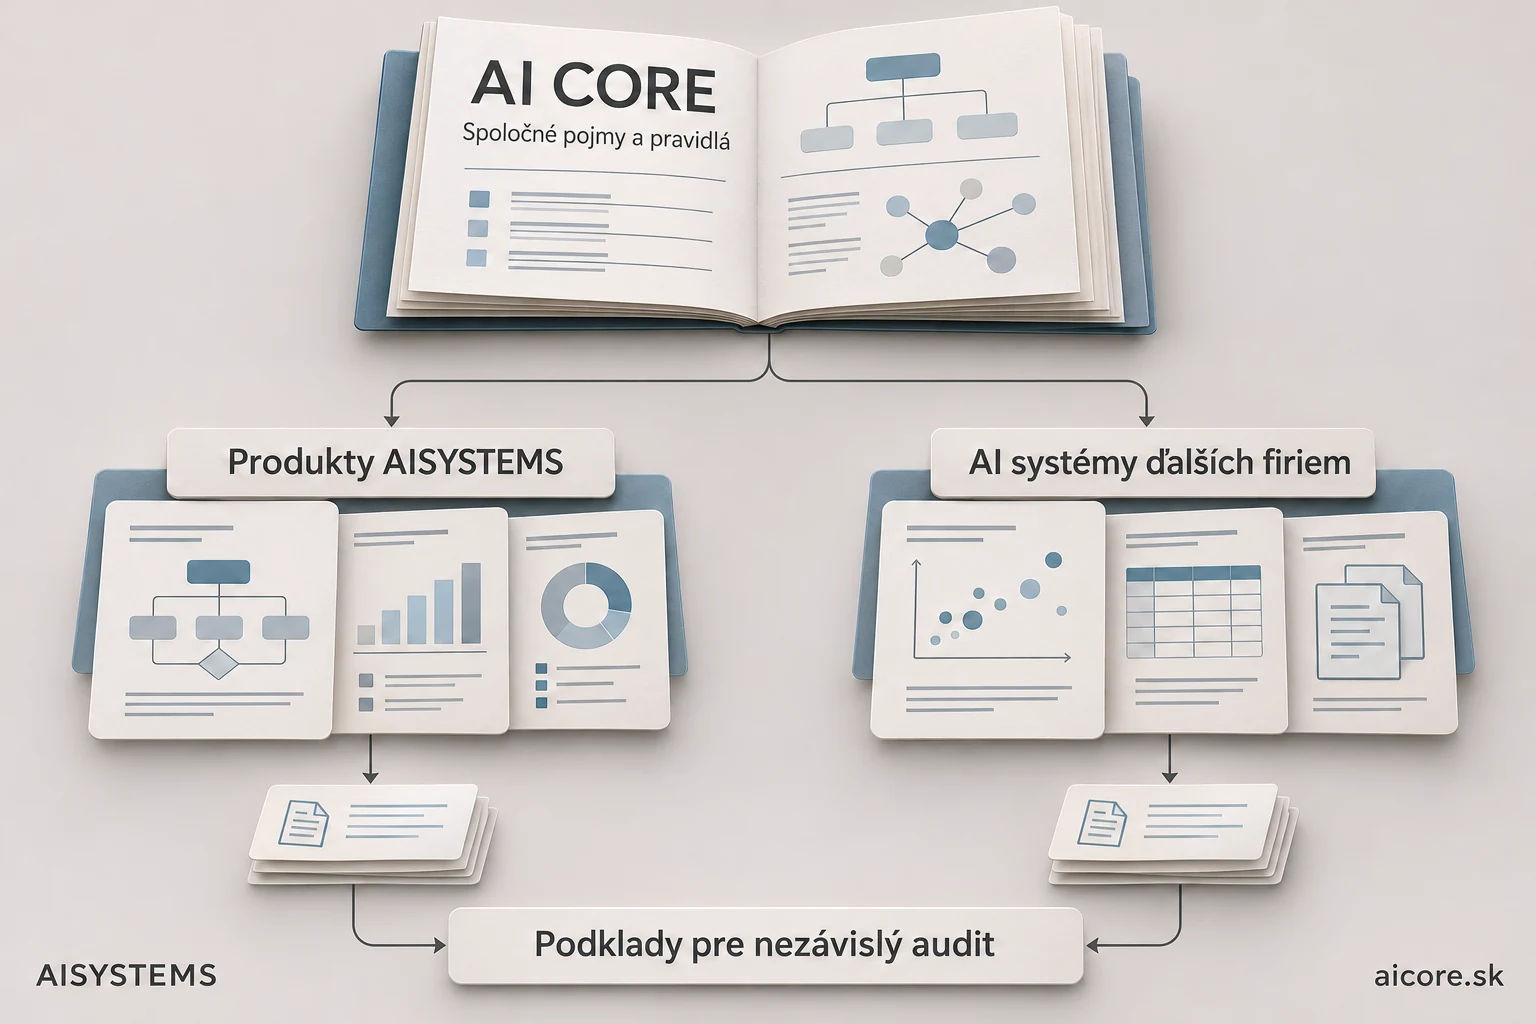
Specific control objectives, methods and evidence requirements. Usable without a proprietary audit program or dependence on a single tool.
Security auditability of a publishing system: public interface boundaries, permissions, publication gates and evidence provenance.
Requirements and assessment plan →Security of assistants with tools: permissions, memory, external inputs, action approval and operational boundaries.
Capability-based requirements →AI CORE provides a framework for evidence. Verification and conclusions remain the assessor’s responsibility.
Select a profile and justify applicability based on the system’s capabilities and risks.
Link actual observations to the relevant control. Missing evidence remains missing evidence.
The assessor selects methods, examines evidence and states the limitations of the assessment.
Readable pages, stable addresses and versioned JSON artifacts describe the same requirements. No hidden instructions or mandatory client.
Concepts, profiles, evidence, integration and release governance. Available in English and Slovak.
Exact versions, addresses, dependencies and checksums.
Selected OWASP requirements, NIST frameworks and W3C provenance concepts.
A stable profile release is neither a certificate nor an assessment result for a particular system. AI CORE does not execute tests or collect private evidence.